
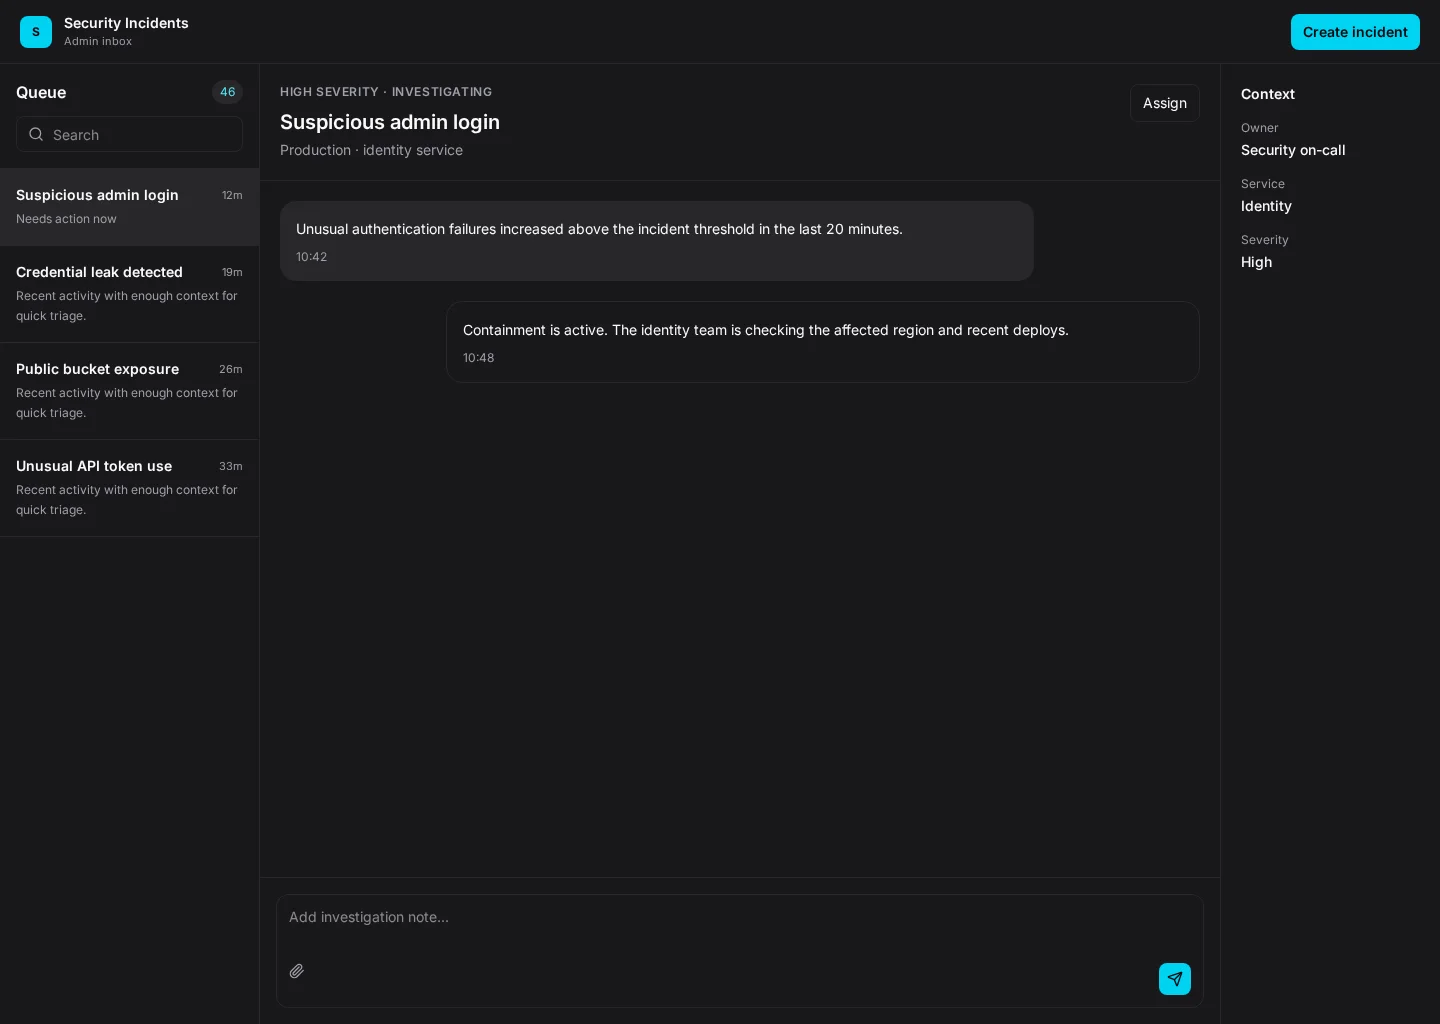
Coordinate active security incidents with severity, owner, affected systems, timeline, evidence, and containment status visible. The screen connects Incidents and Alerts so workspace admins can find the “Create incident” action while checking open and critical.
Use this reference when you need to design this workflow inside an existing product. The example includes practical records such as Suspicious admin login and Credential leak detected, rather than an empty visual shell.
Inbox
Create incident
Inbox
Default, loading, empty, error, permission, success
Adaptable product UI theme
Workspace admins need a clear “Create incident” action without losing sight of open, critical and the affected records. Keep the decision and its outcome clear before moving to the next task.
Incidents → Alerts → Create incident → Review outcome
Inbox, Incidents, Alerts, Systems, accessible states, contextual actions
Keep the active record close to its history, owner and status. Make urgent items easy to find without hiding the rest.
In this design, people should be able to compare Suspicious admin login with Credential leak detected. Make open clear, then use critical to explain whether the next step needs attention.
Before handing this to a designer or engineer, check keyboard focus, error copy, permissions and what happens after they choose the “Create incident” action. The happy path alone is not enough.
Related UI examples: Access Reviews, API Access, Audit Logs.
Design a security incidents screen for our existing software product. Use our real design-system tokens, components and product language. Show Incidents and Alerts, include believable records such as Suspicious admin login, and make create incident easy to find. Map loading, empty, failure, permission and success states before you create editable high-fidelity screens.