
Manage TLS certificates, domains, issuers, environments, expiry dates, renewals, and ownership across services. This example brings Certificates and Domains together so engineering teams can find the next task without losing context.
It includes representative records such as api.figr.design and app.figr.design. Use the screenshot to study the layout, then adapt its components and product states to your own design system.
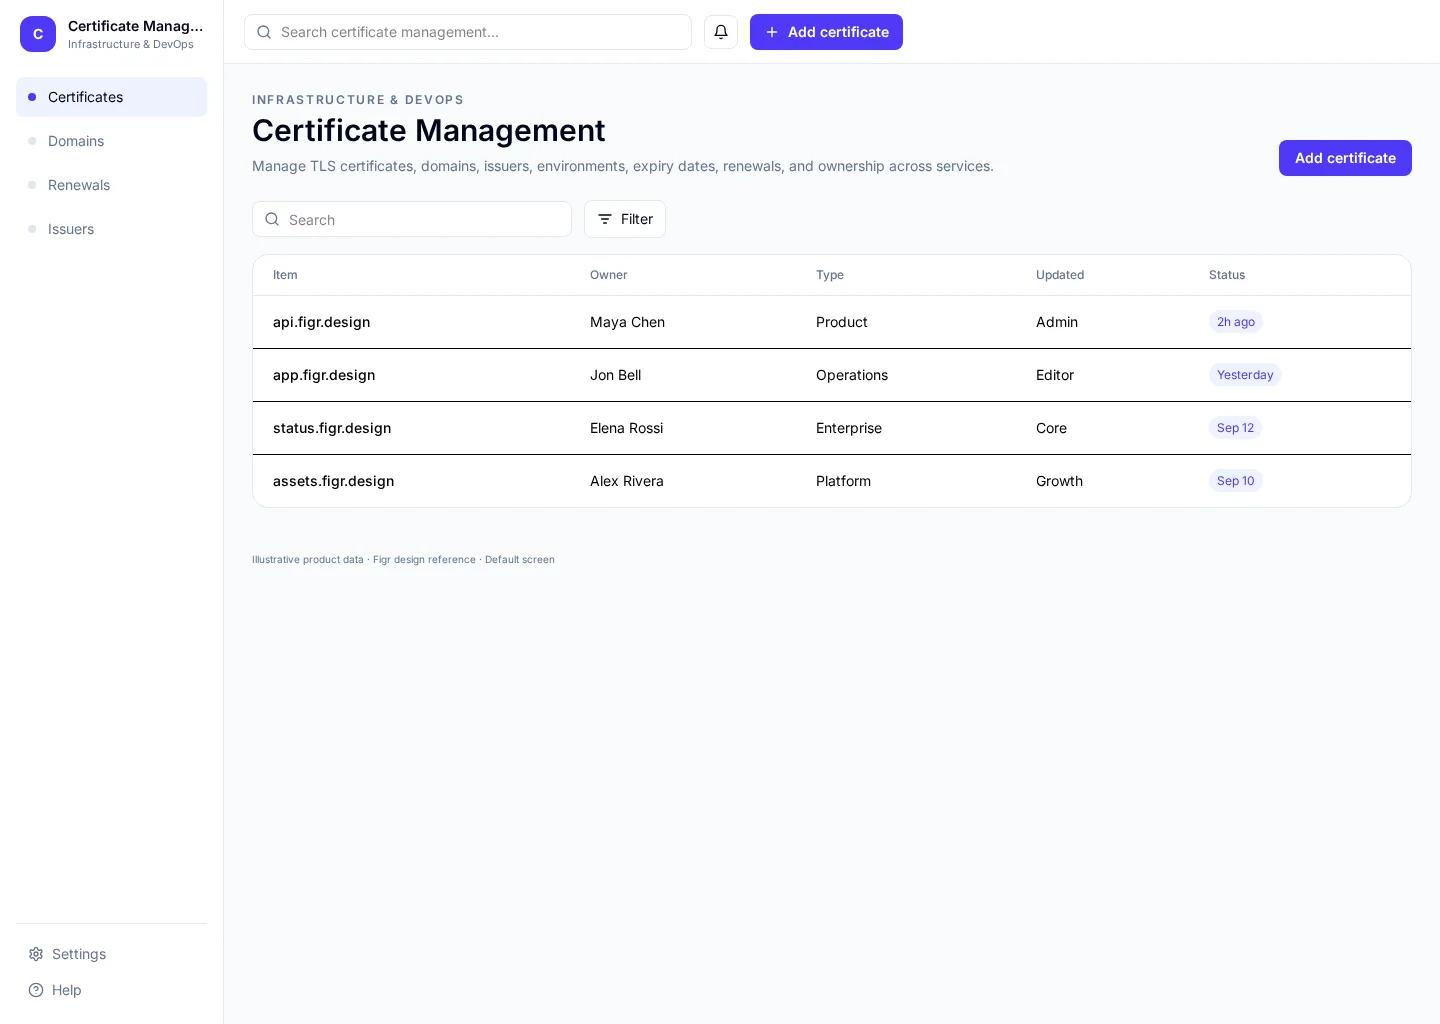
Table
Add certificate
Table
Default, loading, empty, error, permission, success
Configurable product UI theme
Engineering and security teams need to add certificate while keeping certificates, expiring soon and exceptions visible. The interface should show what changed and who should act next.
Certificates → Domains → Add certificate → Review outcome
Table, Certificates, Domains, contextual actions, error recovery
Prioritize columns that help people act. Keep filters when readers drill into details and return; show who owns each unresolved exception.
Pay attention to certificates and domains. People need to distinguish api.figr.design from app.figr.design. Keep certificates visible, especially when a record changes owner or status.
Before this screen reaches handoff, verify keyboard focus, empty and permission states, and what happens after someone chooses “Add certificate”. Make error recovery as clear as the happy path.
Related screen examples to explore next: Job Scheduler, Environment Configuration, Queue Monitor.
Design a certificate management screen inside our existing product. Use our current components, tokens and content language. Include Certificates and Domains views, credible records like api.figr.design, and a clear “Add certificate” action. Use our product permissions and show loading, empty, error and success states. Keep the output editable in Figma.